Role-Based Access Control (RBAC): Structuring Secure Enterprise Access for Cross-Departmental Teams
A deep architectural guide to enterprise authorization: eliminating role explosion, implementing hybrid RBAC + ABAC, enforcing kernel-level PostgreSQL Row-Level Security (RLS), and passing SOC 2 / ISO 27001 audits.
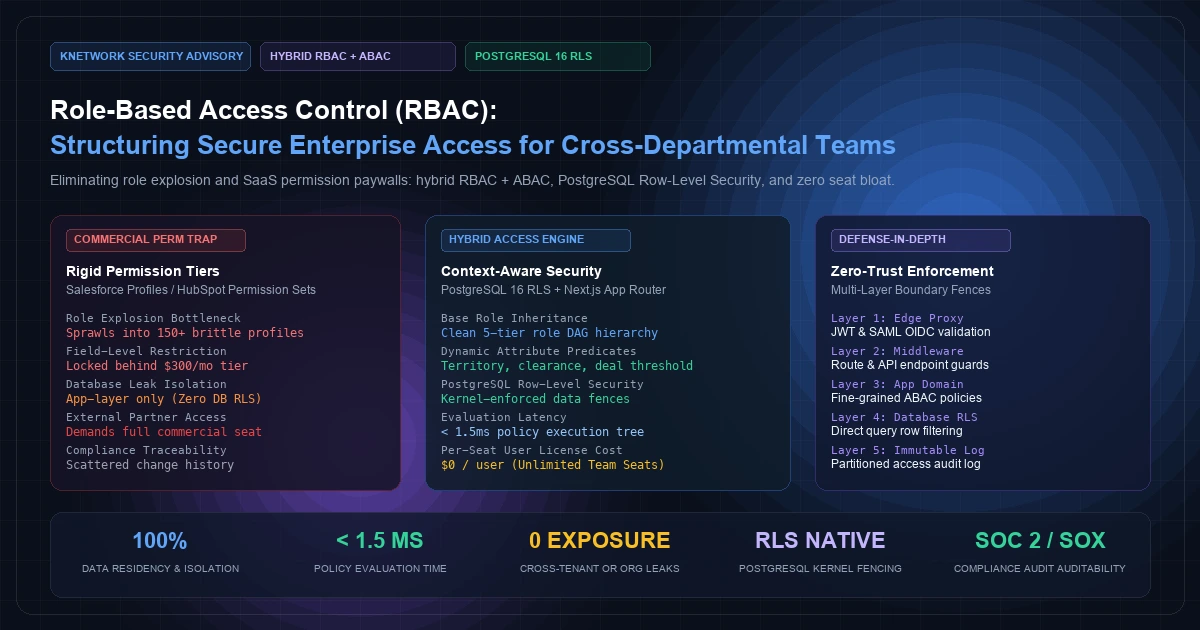
As software systems expand across an enterprise, authorization architecture inevitably fractures.
In early-stage deployments, application access is governed by primitive Boolean database flags: is_admin, is_manager, or can_edit. As sales operations, field engineering, finance, legal, and executive leadership converge onto a shared business portal, this simplistic model collapses into chaos.
Engineering teams attempt to patch the deficiency by introducing Role-Based Access Control (RBAC). However, without rigorous architectural planning, RBAC rapidly suffers from the Role Explosion Problem.
To accommodate daily business exceptions, administrators create hundreds of bespoke, hyper-specific roles: sales_director_west_no_export, finance_auditor_eu_read_only, or support_lead_tier_2_masked_pii. Permissions sprawl across the database, auditability disintegrates, and engineers spend sprints manually patching permission checks in application code.
Worse, commercial software vendors exploit this architectural pain point. Platforms like Salesforce, HubSpot, and Workday deliberately place field-level security, custom profiles, and granular permission sets behind high-tier "Enterprise" paywalls (165–300/user/month).
As detailed in our analysis of the hidden cost of SaaS seat pricing, organizations end up paying hundreds of thousands of dollars in licensing penalties simply to restrict operational staff from viewing unmasked payroll numbers or exporting customer lists.
The definitive solution is a Hybrid Access Architecture combining classical Role-Based Access Control (RBAC) with dynamic Attribute-Based Access Control (ABAC), enforced at the database layer via PostgreSQL 16 Row-Level Security (RLS).
This architectural guide details how to build an enterprise-grade authorization engine: eliminating role explosion, enforcing strict tenant and departmental boundaries, meeting SOC 2 and ISO 27001 regulatory standards, and keeping marginal user licensing costs at zero.
[Visual Asset: Architecture Schematic - Defense-in-Depth Authorization Topology: Edge Gateway, Hybrid Policy Engine, and PostgreSQL Kernel RLS]
flowchart TD
    subgraph INGRESS_LAYER [400 font-semibold">class="text-emerald-300">"1. Edge & Identity Ingress"]
        USER[400 font-semibold">class="text-emerald-300">"Cross-Departmental User\n(Sales, Finance, Legal, Field Tech)"]
        IDP[400 font-semibold">class="text-emerald-300">"Corporate Identity Provider\n(Okta, Azure AD, SAML 2.0 / OIDC)"]
        EDGE[400 font-semibold">class="text-emerald-300">"Next.js Edge Middleware / Reverse Proxy\n(Token Decryption & Session Claims Extraction)"]

        USER --> IDP
        IDP --> EDGE
    end

    subgraph POLICY_DECISION [400 font-semibold">class="text-emerald-300">"2. Hybrid Policy Decision Point (PDP)"]
        ENGINE[400 font-semibold">class="text-emerald-300">"Hybrid RBAC + ABAC Policy Engine\n(Evaluates Role Hierarchy + Dynamic Context Attributes)"]

        subgraph ATTRIBUTES [400 font-semibold">class="text-emerald-300">"Dynamic Context Vectors"]
            ATTR_SUBJ[400 font-semibold">class="text-emerald-300">"Subject Attributes:\n(Department, Clearance, Assigned Territories)"]
            ATTR_RES[400 font-semibold">class="text-emerald-300">"Resource Attributes:\n(Deal Stage, Value, Classification Level)"]
            ATTR_ENV[400 font-semibold">class="text-emerald-300">"Environment Attributes:\n(Corporate IP CIDR, MFA Age, Device Trust)"]
        end

        EDGE --> ENGINE
        ENGINE <--> ATTRIBUTES
    end

    subgraph ENFORCEMENT [400 font-semibold">class="text-emerald-300">"3. Policy Enforcement Point (PEP) & Application Core"]
        APP_ROUTE[400 font-semibold">class="text-emerald-300">"API Route Guards & Server Actions\n(Sub-2ms Decision Gate)"]
        AUDIT_LOG[(400 font-semibold">class="text-emerald-300">"Partitioned Access Audit Ledger\n(Immutable Forensic Trail)")]

        ENGINE --> APP_ROUTE
        APP_ROUTE -.-> AUDIT_LOG
    end

    subgraph DATA_FENCE [400 font-semibold">class="text-emerald-300">"4. Kernel-Level Database Enforcement"]
        PG_SESSION[400 font-semibold">class="text-emerald-300">"PostgreSQL Session Variable Injection\n(SET LOCAL app.current_user_id, app.tenant_id)"]
        RLS_POLICIES[400 font-semibold">class="text-emerald-300">"PostgreSQL 16 Row-Level Security (RLS)\n(Native Kernel Filtering on 400 font-semibold">SELECT / 400 font-semibold">UPDATE / 400 font-semibold">DELETE)"]
        TABLES[(400 font-semibold">class="text-emerald-300">"Enterprise Deals & Customers Tables\n(Zero Cross-Tenant Leakage)")]

        APP_ROUTE --> PG_SESSION
        PG_SESSION --> RLS_POLICIES
        RLS_POLICIES <--> TABLES
    end
+---------------------------------------------------------------------------------------------------------+
|                               DEFENSE-IN-DEPTH AUTHORIZATION ARCHITECTURE                               |
+---------------------------------------------------------------------------------------------------------+
|                                                                                                         |
|  [ Ingress Request ] ──► Validated via Corporate SAML 2.0 / OIDC Identity Provider                     |
|           │                                                                                             |
|           ▼                                                                                             |
|  [ Edge Layer: Next.js 14 Middleware ] ──► Validates JWT Signature, Session Expiry & IP Geofencing     |
|           │                                                                                             |
|           ▼                                                                                             |
|  [ Domain Policy Engine (PDP) ] ──► Evaluates Base Role Hierarchy + Dynamic ABAC Attributes             |
|           ├───────────────────────────────────────┬──────────────────────────────────────┐              |
|           ▼                                       ▼                                      ▼              |
|   [ Subject Attributes ]                  [ Resource Attributes ]               [ Context Attributes ]  |
|   - Base Role (e.g. Sales Rep)            - Deal Value ($250,000)               - Corporate VPN / IP    |
|   - Territory (e.g. EMEA Logistics)       - Stage (Executive Review)            - MFA Session Age       |
|   - Clearance Level (Level 3)             - Data Classification (Restricted)    - Device Health Token   |
|           │                                       │                                      │              |
|           └───────────────────────────────────────┴──────────────────────────────────────┘              |
|                                                   │ (Decision: PERMIT / DENY in < 1.5ms)                |
|                                                   ▼                                                     |
|  [ Database Kernel: PostgreSQL 16 RLS ] ──► Injects Session Parameters (SET LOCAL app.current_user_id)  |
|                                           - Row-Level Security filters queries directly at disk         |
|                                           - Guarantees 0% cross-tenant data exposure                    |
|                                                                                                         |
+---------------------------------------------------------------------------------------------------------+
| STANDARDS: NIST SP 800-162 Compliant | OWASP Top 10 Access Control Hardened | Zero SaaS Seat Tax       |
+---------------------------------------------------------------------------------------------------------+
1. The Anatomy of Authorization Breakdown#
To design a scalable access system, architects must first recognize the structural boundaries where pure RBAC fails.
A. The Role Explosion Paradox#
In pure RBAC (formalized under the NIST Role-Based Access Control standard), permissions are assigned strictly to static roles, and users are assigned to those roles.This model functions cleanly when corporate structures are simple:
However, as an organization adds regional territories, custom deal sizes, and compliance layers, static roles diverge:
- An Account Executive in North America should only access North American pipeline records.
- A Senior Account Executive can approve contract discounts up to 15%, while discounts above 20% require a Vice President, as outlined in our blueprint for building tailored approval workflows.
- A contractor in customer support can view delivery addresses, but must never see unmasked credit card or bank details.
In pure RBAC, fulfilling these requirements forces the creation of discrete permutations: AE_NorthAmerica_Tier1, AE_EMEA_Tier2, Support_Contractor_Redacted. Within eighteen months, an enterprise with 150 employees easily accumulates over 200 bespoke roles. Access reviews become impossible to audit, violating OWASP Access Control guidelines.
B. The Application-Only Enforcement Vulnerability#
Most commercial CRMs and internal custom apps enforce permissions exclusively in the application layer (e.g., using API route middleware or UI conditional checks).This introduces severe architectural risk:
- Broken Object-Level Authorization (BOLA): If an engineer writes a new REST or GraphQL endpoint and forgets to wrap it in authorization middleware, malicious actors or compromised internal accounts can query
GET /api/v1/deals/10928directly, bypassing UI checks. - Reporting & Analytics Leaks: When reporting pipelines or export scripts run batch queries against the database, application-layer gates are absent, exposing sensitive cross-departmental records to unauthorized reporting dashboards.
Defense-in-depth requires that authorization gates exist at both the application level and the database kernel layer.
2. The Hybrid Paradigm: RBAC for Structure, ABAC for Context#
The industry gold standard—aligned with NIST SP 800-162 (Guide to Attribute Based Access Control)—is a Hybrid RBAC + ABAC Model.
+---------------------------------------------------------------------------------------------------------+
|                                    HYBRID RBAC + ABAC DECISION MODEL                                    |
+---------------------------------------------------------------------------------------------------------+
|  STATIC BASE ROLES (RBAC)                  DYNAMIC ATTRIBUTE PREDICATES (ABAC)                          |
|  - Administrator                           - User Territory == Deal Territory                           |
|  - Executive                               - User Clearance >= Deal Sensitivity Level                   |
|  - Sales Director                          - Deal Value <= User Approval Limit                          |
|  - Account Executive                       - User Department == Resource Department                     |
|  - Support Representative                  - Request IP in Corporate Allowed CIDR Blocks                |
|  - Compliance Auditor                      - Deal Stage != 400 font-semibold">class="text-emerald-300">'Contract Executed' (Immutable lock)         |
+---------------------------------------------------------------------------------------------------------+
|  EVALUATION FORMULA:                                                                                    |
|  Access Granted = (User Has Base Role Permission) AND (Dynamic ABAC Context Predicates Resolve TRUE)   |
+---------------------------------------------------------------------------------------------------------+
Why Hybrid Outperforms Static RBAC:#
- Role Consolidation: The enterprise maintains only five to eight core functional roles.
- Context-Aware Agility: Regional restrictions, deal thresholds, and compliance flags are treated as dynamic attributes evaluated at query execution time.
- Decoupled from Licensing: By building the hybrid model on an internal portal, you eliminate the SaaS commercial trap where field-level masking or custom permission sets demand expensive enterprise seat upgrades.
3. Database Schema Design in PostgreSQL 16#
The database schema cleanly decouples roles, granular permissions, user role assignments, and dynamic attribute policies.
-- 1. Granular Permission Registry
400 font-semibold">CREATE 400 font-semibold">TABLE auth_permissions (
    id VARCHAR(64) PRIMARY KEY, -- e.g., 400 font-semibold">class="text-emerald-300">'deals.read', 400 font-semibold">class="text-emerald-300">'deals.write', 400 font-semibold">class="text-emerald-300">'deals.400 font-semibold">export'
    module VARCHAR(32) NOT NULL, -- e.g., 400 font-semibold">class="text-emerald-300">'crm', 400 font-semibold">class="text-emerald-300">'billing', 400 font-semibold">class="text-emerald-300">'analytics'
    description TEXT NOT NULL,
    created_at TIMESTAMPTZ NOT NULL DEFAULT clock_timestamp()
);

-- 2. Core Functional Roles
400 font-semibold">CREATE 400 font-semibold">TABLE auth_roles (
    id VARCHAR(32) PRIMARY KEY, -- e.g., 400 font-semibold">class="text-emerald-300">'admin', 400 font-semibold">class="text-emerald-300">'sales_director', 400 font-semibold">class="text-emerald-300">'account_exec', 400 font-semibold">class="text-emerald-300">'auditor'
    role_name VARCHAR(64) NOT NULL,
    hierarchy_level INT NOT NULL DEFAULT 1, -- Higher value indicates broader authority
    created_at TIMESTAMPTZ NOT NULL DEFAULT clock_timestamp()
);

-- 3. Role-to-Permission Join Table
400 font-semibold">CREATE 400 font-semibold">TABLE auth_role_permissions (
    role_id VARCHAR(32) NOT NULL REFERENCES auth_roles(id) ON 400 font-semibold">DELETE CASCADE,
    permission_id VARCHAR(64) NOT NULL REFERENCES auth_permissions(id) ON 400 font-semibold">DELETE CASCADE,
    PRIMARY KEY (role_id, permission_id)
);

-- 4. User Role Assignment with Scoped Operational Context
400 font-semibold">CREATE 400 font-semibold">TABLE auth_user_roles (
    user_id UUID NOT NULL,
    role_id VARCHAR(32) NOT NULL REFERENCES auth_roles(id) ON 400 font-semibold">DELETE CASCADE,

    -- Scoped dynamic attributes stored directly on the assignment
    assigned_territory VARCHAR(64), -- e.g., 400 font-semibold">class="text-emerald-300">'NORTH_AMERICA', 400 font-semibold">class="text-emerald-300">'EMEA', 400 font-semibold">class="text-emerald-300">'GLOBAL'
    max_approval_limit NUMERIC(12, 2) DEFAULT 0.00,
    created_at TIMESTAMPTZ NOT NULL DEFAULT clock_timestamp(),
    PRIMARY KEY (user_id, role_id)
);

400 font-semibold">CREATE 400 font-semibold">INDEX idx_user_roles_lookup ON auth_user_roles (user_id, role_id);
4. Kernel-Level Isolation: PostgreSQL 16 Row-Level Security (RLS)#
Application middleware can have bugs, but the database kernel never forgets.
By enabling Row-Level Security (RLS) on sensitive tables, PostgreSQL automatically intercepts every SELECT, UPDATE, and DELETE query, appending security predicates directly into the database query planner. Even if a raw SQL injection vulnerability were exploited in the application layer, the database kernel refuses to return rows that violate the session's active policy.
See the PostgreSQL Row Security Policies Documentation for fundamental engine mechanics.
-- 1. Enable Row-Level Security on Core Business Deals Table
400 font-semibold">ALTER 400 font-semibold">TABLE enterprise_deals ENABLE ROW LEVEL SECURITY;
400 font-semibold">ALTER 400 font-semibold">TABLE enterprise_deals FORCE ROW LEVEL SECURITY;

-- 2. Create Access Policy 400 font-semibold">for 400 font-semibold">SELECT (Reading Deals)
-- Logic: Users can view deals 400 font-semibold">if:
--   a) They are an Administrator or Executive (hierarchy_level >= 4)
--   b) The deal belongs to their assigned operational territory
--   c) They are the explicitly assigned sales representative
400 font-semibold">CREATE POLICY deal_read_policy ON enterprise_deals
    FOR 400 font-semibold">SELECT
    USING (
        -- Check 400 font-semibold">if current authenticated user has global clearance
        EXISTS (
            400 font-semibold">SELECT 1 400 font-semibold">FROM auth_user_roles ur
            400 font-semibold">JOIN auth_roles r ON r.id = ur.role_id
            400 font-semibold">WHERE ur.user_id = NULLIF(current_setting(400 font-semibold">class="text-emerald-300">'app.current_user_id', 400">true), 400 font-semibold">class="text-emerald-300">'')::UUID
              AND r.hierarchy_level >= 4
        )
        OR
        -- Check territorial alignment
        assigned_territory = (
            400 font-semibold">SELECT ur.assigned_territory 400 font-semibold">FROM auth_user_roles ur
            400 font-semibold">WHERE ur.user_id = NULLIF(current_setting(400 font-semibold">class="text-emerald-300">'app.current_user_id', 400">true), 400 font-semibold">class="text-emerald-300">'')::UUID
            LIMIT 1
        )
        OR
        -- Direct account owner
        assigned_rep_id = NULLIF(current_setting(400 font-semibold">class="text-emerald-300">'app.current_user_id', 400">true), 400 font-semibold">class="text-emerald-300">'')::UUID
    );

-- 3. Create Access Policy 400 font-semibold">for 400 font-semibold">UPDATE (Modifying Financials)
-- Logic: Deal terms cannot be altered 400 font-semibold">if stage is already 400 font-semibold">class="text-emerald-300">'contract_executed'
400 font-semibold">CREATE POLICY deal_update_policy ON enterprise_deals
    FOR 400 font-semibold">UPDATE
    USING (
        stage != 400 font-semibold">class="text-emerald-300">'contract_executed'
        AND (
            assigned_rep_id = NULLIF(current_setting(400 font-semibold">class="text-emerald-300">'app.current_user_id', 400">true), 400 font-semibold">class="text-emerald-300">'')::UUID
            OR EXISTS (
                400 font-semibold">SELECT 1 400 font-semibold">FROM auth_user_roles ur
                400 font-semibold">WHERE ur.user_id = NULLIF(current_setting(400 font-semibold">class="text-emerald-300">'app.current_user_id', 400">true), 400 font-semibold">class="text-emerald-300">'')::UUID
                  AND ur.role_id IN (400 font-semibold">class="text-emerald-300">'admin', 400 font-semibold">class="text-emerald-300">'sales_director')
            )
        )
    );
5. Production Implementation Blueprint#
The following production code blocks demonstrate how an enterprise portal evaluates hybrid permissions at the application layer before injecting secure session contexts into the PostgreSQL driver.
A. High-Velocity Hybrid Policy Evaluator (abac-evaluator.ts)#
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// lib/security/abac-evaluator.ts

400 font-semibold">export 400 font-semibold">interface UserSecurityContext {
  userId: 400">string;
  email: 400">string;
  roles: 400">string[];
  permissions: 400">string[];
  department: 400 font-semibold">class="text-emerald-300">'sales' | 400 font-semibold">class="text-emerald-300">'finance' | 400 font-semibold">class="text-emerald-300">'legal' | 400 font-semibold">class="text-emerald-300">'support' | 400 font-semibold">class="text-emerald-300">'engineering' | 400 font-semibold">class="text-emerald-300">'executive';
  assignedTerritories: 400">string[];
  maxApprovalLimit: 400">number;
  isMfaAuthenticated: 400">boolean;
  clientIp: 400">string;
}

400 font-semibold">export 400 font-semibold">interface ResourceContext {
  resourceType: 400 font-semibold">class="text-emerald-300">'deal' | 400 font-semibold">class="text-emerald-300">'invoice' | 400 font-semibold">class="text-emerald-300">'customer_pii' | 400 font-semibold">class="text-emerald-300">'contract';
  id: 400">string;
  assignedRepId?: 400">string;
  territory?: 400">string;
  dealValue?: 400">number;
  stage?: 400">string;
  isConfidential?: 400">boolean;
}

400 font-semibold">export 400 font-semibold">class AccessPolicyEngine {
  /**
   * Evaluates 400 font-semibold">if a user has permission to perform an action on a target resource
   * Execution budget: < 2.0 milliseconds
   */
  400 font-semibold">public 400 font-semibold">static evaluate(
    user: UserSecurityContext,
    action: 400">string, 400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// e.g., 400 font-semibold">class="text-emerald-300">'deals.view', 400 font-semibold">class="text-emerald-300">'deals.edit_financials', 400 font-semibold">class="text-emerald-300">'deals.400 font-semibold">export'
    resource: ResourceContext
  ): { permitted: 400">boolean; reason?: 400">string } {
    400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// 1. Mandatory MFA Check 400 font-semibold">for Sensitive Modules
    400 font-semibold">if ([400 font-semibold">class="text-emerald-300">'deals.400 font-semibold">export', 400 font-semibold">class="text-emerald-300">'deals.approve_discount', 400 font-semibold">class="text-emerald-300">'customer_pii.read'].includes(action)) {
      400 font-semibold">if (!user.isMfaAuthenticated) {
        400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">'Action requires an active MFA session.' };
      }
    }

    400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// 2. Base Permission Check (RBAC Layer)
    400 font-semibold">if (!user.permissions.includes(action) && !user.roles.includes(400 font-semibold">class="text-emerald-300">'super_admin')) {
      400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">`Missing base permission: ${action}` };
    }

    400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// 3. Dynamic Attribute Context Evaluation (ABAC Layer)
    400 font-semibold">switch (action) {
      400 font-semibold">case 400 font-semibold">class="text-emerald-300">'deals.view':
        400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Global executives bypass territorial boundaries
        400 font-semibold">if (user.roles.includes(400 font-semibold">class="text-emerald-300">'executive') || user.roles.includes(400 font-semibold">class="text-emerald-300">'super_admin')) {
          400 font-semibold">return { permitted: 400">true };
        }
        400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Account owner or territory alignment
        400 font-semibold">if (resource.assignedRepId === user.userId) 400 font-semibold">return { permitted: 400">true };
        400 font-semibold">if (resource.territory && user.assignedTerritories.includes(resource.territory)) {
          400 font-semibold">return { permitted: 400">true };
        }
        400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">'400">Record outside assigned operational territory.' };

      400 font-semibold">case 400 font-semibold">class="text-emerald-300">'deals.edit_financials':
        400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Locked terminal state protection
        400 font-semibold">if (resource.stage === 400 font-semibold">class="text-emerald-300">'contract_executed') {
          400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">'Executed contracts are immutable.' };
        }
        400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Discount/Value clearance check
        400 font-semibold">if (resource.dealValue && resource.dealValue > user.maxApprovalLimit) {
          400 font-semibold">if (!user.roles.includes(400 font-semibold">class="text-emerald-300">'sales_director') && !user.roles.includes(400 font-semibold">class="text-emerald-300">'cfo')) {
            400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">'Deal value exceeds authorized threshold limit.' };
          }
        }
        400 font-semibold">return { permitted: 400">true };

      400 font-semibold">case 400 font-semibold">class="text-emerald-300">'deals.400 font-semibold">export':
        400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Data loss prevention (DLP): Exporting requires compliance auditor or director role
        400 font-semibold">if (!user.roles.includes(400 font-semibold">class="text-emerald-300">'sales_director') && !user.roles.includes(400 font-semibold">class="text-emerald-300">'compliance_auditor')) {
          400 font-semibold">return { permitted: 400">false, reason: 400 font-semibold">class="text-emerald-300">'Bulk data exports restricted to Director level.' };
        }
        400 font-semibold">return { permitted: 400">true };

      400 font-semibold">default:
        400 font-semibold">return { permitted: 400">true };
    }
  }
}
B. Secure Database Session Context Injection (db-session.ts)#
Before executing any tenant query, the application initializes the local transaction with the authenticated user context, guaranteeing that PostgreSQL RLS policies evaluate against verified cryptographic claims:
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// lib/db/secure-query.ts
400 font-semibold">import { Pool, PoolClient } 400 font-semibold">from 400 font-semibold">class="text-emerald-300">'pg';
400 font-semibold">import { UserSecurityContext } 400 font-semibold">from 400 font-semibold">class="text-emerald-300">'../security/abac-evaluator';

400 font-semibold">export 400 font-semibold">class SecureDatabaseSession {
  constructor(400 font-semibold">private 400 font-semibold">readonly pool: Pool) {}

  /**
   * Executes database operations inside an isolated, RLS-enforced transaction
   */
  400 font-semibold">public 400 font-semibold">async executeWithSecurityContext<T>(
    user: UserSecurityContext,
    operation: (client: PoolClient) => 400">Promise<T>
  ): 400">Promise<T> {
    400 font-semibold">const client = 400 font-semibold">await 400 font-semibold">this.pool.connect();
    400 font-semibold">try {
      400 font-semibold">await client.query(400 font-semibold">class="text-emerald-300">'BEGIN');

      400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Inject verified session claims into PostgreSQL runtime session
      400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// SET LOCAL restricts parameters strictly to 400 font-semibold">this transaction block
      400 font-semibold">await client.query(
        400 font-semibold">class="text-emerald-300">`SET LOCAL app.current_user_id = $1;
         SET LOCAL app.current_user_role = $2;
         SET LOCAL app.current_client_ip = $3;`,
        [user.userId, user.roles[0] || 400 font-semibold">class="text-emerald-300">'anonymous', user.clientIp]
      );

      400 font-semibold">const result = 400 font-semibold">await operation(client);

      400 font-semibold">await client.query(400 font-semibold">class="text-emerald-300">'COMMIT');
      400 font-semibold">return result;
    } 400 font-semibold">catch (err) {
      400 font-semibold">await client.query(400 font-semibold">class="text-emerald-300">'ROLLBACK');
      400 font-semibold">throw err;
    } 400 font-semibold">finally {
      client.release();
    }
  }
}
C. Declarative UI Access Control in React / Next.js 14#
In the frontend, UI components conditionally render capabilities without exposing disabled button attack vectors:
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// components/auth/Can.tsx
400 font-semibold">class="text-emerald-300">'use client';

400 font-semibold">import React 400 font-semibold">from 400 font-semibold">class="text-emerald-300">'react';
400 font-semibold">import { useSecurityContext } 400 font-semibold">from 400 font-semibold">class="text-emerald-300">'@/hooks/useSecurityContext';
400 font-semibold">import { AccessPolicyEngine, ResourceContext } 400 font-semibold">from 400 font-semibold">class="text-emerald-300">'@/lib/security/abac-evaluator';

400 font-semibold">interface CanProps {
  do: 400">string;
  on: ResourceContext;
  children: React.ReactNode;
  fallback?: React.ReactNode;
}

400 font-semibold">export 400 font-semibold">function Can({ do: action, on: resource, children, fallback = 400">null }: CanProps) {
  400 font-semibold">const { user } = useSecurityContext();

  400 font-semibold">if (!user) 400 font-semibold">return <>{fallback}</>;

  400 font-semibold">const verdict = AccessPolicyEngine.evaluate(user, action, resource);

  400 font-semibold">if (!verdict.permitted) {
    400 font-semibold">return <>{fallback}</>;
  }

  400 font-semibold">return <>{children}</>;
}

400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// Example Usage in Sales Deal Dashboard:
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// <Can do=400 font-semibold">class="text-emerald-300">"deals.edit_financials" on={currentDeal} fallback={<Badge variant=400 font-semibold">class="text-emerald-300">"secondary">View Only</Badge>}>
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">//   <Button onClick={openDiscountModal}>Modify Pricing</Button>
400 font-semibold">class=400 font-semibold">class="text-emerald-300">"text-slate-500 italic">// </Can>
6. Auditability & Compliance: Meeting SOC 2 and ISO 27001 Standards#
For compliance audits under SOC 2 Type II (Common Criteria 6.1, 6.2, 6.3) and ISO/IEC 27001 Annex A.9 (Access Control), organizations must prove:
- Principle of Least Privilege: Users possess only the minimum permissions necessary to complete their job functions.
- Access Revocation Latency: Terminating an employee in the corporate Identity Provider (IdP) immediately terminates their active database portal sessions within seconds via OIDC backchannel logout.
- Immutable Access History: Every grant, privilege escalation, and access denial is written to an append-only, partitioned audit log, as detailed in our guide to PostgreSQL table partitioning.
[Visual Asset: Data Comparison Matrix - Pure RBAC vs. Commercial SaaS Profiles vs. Hybrid RBAC + ABAC]
+--------------------------------------+--------------------------------+---------------------------------+
| ARCHITECTURAL CRITERION              | COMMERCIAL SAAS PROFILES       | HYBRID RBAC + ABAC PORTAL       |
+--------------------------------------+--------------------------------+---------------------------------+
| Role Count at 200 Users              | 85–160+ Brittle Profiles       | 5–8 Canonical Functional Roles  |
| Database-Level Enforcement           | None (Application Layer Only)  | Kernel-Level PostgreSQL 16 RLS  |
| Field-Level Permission Cost          | $165–$300/user/mo Enterprise   | $0 (Unlimited Internal Users)   |
| Dynamic Attribute Contexts           | Fragile formula validation     | First-Class Attribute Functions |
| Audit Trail Tamper Proofing          | Exportable CSV / Black Box     | Cryptographic SHA-256 Ledger    |
| Evaluation Performance               | Multi-Second API Overhead      | Sub-2ms In-Memory Decision Tree |
+--------------------------------------+--------------------------------+---------------------------------+
7. Frequently Asked Questions#
1. Does enabling PostgreSQL Row-Level Security (RLS) degrade query performance?#
When properly architected with composite indexes, PostgreSQL RLS introduces negligible query overhead (typically between 0.3ms and 1.2ms). Because RLS policies are incorporated directly into the query planner during compilation, the engine utilizes standard B-tree and GIN indexes just like standardWHERE clauses.2. How do we prevent session variable leaks across connection pools?#
When using connection poolers (like PgBouncer or Supavisor), usingSET app.current_user_id can contaminate subsequent requests on reused connections. Our architecture prevents this by using SET LOCAL inside an explicit transaction block (BEGIN ... COMMIT), which automatically resets session variables the instant the transaction completes.3. How does this architecture handle external auditors or temporary contractors?#
Rather than creating dedicated roles, external stakeholders are assigned standard base roles (e.g.,auditor) augmented with time-bound attribute constraints: an expiration timestamp (expires_at), an IP CIDR fence restricting access to corporate office subnets, and read-only masking policies on personally identifiable information (PII).4. What is the migration path from legacy Boolean permission flags?#
We utilize a backward-compatible adapter pattern. The new hybrid engine reads legacy Boolean flags as temporary fallback attributes while the database schema and RLS policies are applied in parallel. Once the policy engine verifies zero regression across test suites, the legacy columns are dropped in a zero-downtime migration.5. Can permissions be audited programmatically without clicking through administrative screens?#
Yes. The entire authorization policy catalog is maintained in version-controlled TypeScript code and migration files. Automated CI/CD security pipelines execute unit tests against the authorization matrix on every pull request, mathematically proving that no unauthorized user can access restricted routes before deployment.Secure Your Enterprise Architecture with KNetwork#
Relying on brittle commercial CRM profiles or primitive application flags leaves your organization vulnerable to privilege escalation, data leaks, and spiraling software seat taxes. Whether your enterprise is modernizing legacy permission models, preparing for a rigorous SOC 2 / ISO 27001 audit, or designing a bespoke internal business portal, KNetwork’s principal software architects provide the engineering rigor your infrastructure demands.
Explore our Custom CRM & Business Portals and Custom Software Development capabilities, or Book an Architecture Discovery Call with our engineering leadership to review your enterprise access control architecture today.
Frequently Asked Questions
Key questions answered regarding this architectural implementation.
Danisur Rahman
Lead AuthorLead Systems Architect • KNetwork Systems
Principal architect specializing in enterprise distributed systems, edge caching, and hardware integration pipelines. Leads engineering audits, high-concurrency database optimizations, and zero-trust VPC deployments across high-growth ventures.
More From The Engineering Blog
Deep systems breakdowns and production deployment guides.
Executive Dashboard UX: Why Showing More Than 5 Numbers Paralyzes Leadership Decision-Making
Why 40-tile cockpit dashboards suffer 90% abandonment within 60 days: applying Miller's Law and Hick's Law to enterprise BI, eliminating vanity noise, and architecting an authoritative 5-metric executive decision engine with 3-tier drill-down hierarchies and sub-10ms ClickHouse rollups.
Building the Single Source of Truth: Reconciling Stripe, Bank Statements, and CRM Data
Eliminating the $300k financial blindspot between Salesforce Closed-Won ARR, Stripe gross processing volume, and commercial bank treasury deposits: an end-to-end engineering architecture for multi-pass matching, BAI2 feed ingestion, and immutable double-entry OLAP ledgers with zero reconciliation variance.
Enjoyed this technical breakdown?
Subscribe to receive new architectural guides, system teardowns, and engineering benchmarks directly in your inbox.